Photo via Times of India

Meet Harsh Jaiswal, Mohan Pedhapati and Rahul Maini: 3 Indian-origin researchers who used Claude to breach OpenAI systems, won $6,500 bounty

Read the original at Times of India ↗
Cite

TOI World Desk. (2026, September 18). Meet Harsh Jaiswal, Mohan Pedhapati and Rahul Maini: 3 Indian-origin researchers who used Claude to breach OpenAI systems, won $6,500 bounty. Times of India. https://timesofindia.indiatimes.com/world/us/meet-harsh-jaiswal-mohan-pedhapati-and-rahul-maini-3-indian-origin-researchers-who-used-claude-to-breach-openai-systems-won-6500-bounty/articleshow/134338838.cms

Dated when The Aporia collected the article, usually within hours of publication. Check the original for its exact date and byline.

Times of India · collected 2026-09-18 · by TOI World Desk

Quick Summary

Cybersecurity researchers Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini from Hacktron AI used Anthropic's Claude AI to uncover and exploit vulnerabilities in OpenAI’s systems, gaining access to employee accounts and an internal code repository within 72 hours. They spent less than $3,000 on AI tokens and were awarded a $6,500 bounty by OpenAI for responsibly disclosing their findings. The attack began with exploiting a vulnerability in Discourse's image-processing software at OpenAI’s community forum, allowing them to chain this with other weaknesses to penetrate further into the system.
Written by AI on 2026-09-18, from this article's own text only (the story summary below draws on all the coverage).
See how they differ ↓

AI analysis

Story summary

In September, cybersecurity researchers at Hacktron AI used Anthropic’s Claude chatbot to breach OpenAI’s internal systems, gaining access to employee accounts and an internal GitHub repository. The researchers discovered a flaw in OpenAI's public help forum hosted by Discourse, which they exploited within 72 hours. They reported the issue immediately, and OpenAI fixed it within 14 hours while paying Hacktron a $6,500 bounty. The incident highlights how quickly AI can be repurposed for cyberattacks, despite efforts to ensure ethical use through bug-hunting programs like this one.

Written for “AI Breach Risks” on 2026-11-21, grounded in this article and the 7 other(s) covering the same event.

How they differ

7 outlets covered “AI Breach Risks”.

What each outlet says

One AI summary per outlet of its latest article on this story, written from that article alone and checked against it. Open the article for the outlet's own words.

Times of IndiaThis outlet18 Sep

Cybersecurity researchers Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini from Hacktron AI used Anthropic's Claude AI to uncover and exploit vulnerabilities in OpenAI’s systems, gaining access to employee accounts and an internal code repository within 72 hours. They spent less than $3,000 on AI tokens and were awarded a $6,500 bounty by OpenAI for responsibly disclosing their findings. The attack began with…

Meet Harsh Jaiswal, Mohan Pedhapati and Rahul Maini: 3 Indian-origin researchers who used Claude to breach OpenAI systems, won $6,500 bounty (this article)
CBS News19 Sep

Hacktron AI researchers claim to have exploited vulnerabilities in OpenAI's ChatGPT using Anthropic's Claude tool. The report, covered by CBS News MoneyWatch's Megan Cerullo, highlights the security concerns surrounding large language models.

Researchers report using Anthropic's Claude to hack OpenAI's ChatGPT →2 articles from CBS News on this story
Semafor18 Sep

Researchers utilized Anthropic’s Claude technology to successfully breach OpenAI’s ChatGPT systems, highlighting the immediate cybersecurity threats posed by advanced AI tools. The incident, which was part of a bug-hunting initiative, underscores growing concerns among business leaders and former government officials about AI-facilitated cyberattacks targeting critical infrastructure. According to recent research…

AI cybersecurity risks explode as Claude used to break into ChatGPT →
The Guardian18 Sep

Cybersecurity researchers at Hacktron AI exploited OpenAI’s systems using Anthropic’s Claude chatbot, gaining access to ChatGPT accounts through an OpenAI staff forum. The hack, conducted under OpenAI's ethical hacking program and reported by the Wall Street Journal, resulted in a $6,500 reward for Hacktron. Researchers noted that advanced AI tools like Claude simplified what was once a complex task, reducing…

OpenAI ‘ethically hacked’ with help of Anthropic’s Claude chatbot →
The Straits Times18 Sep

On September 18, researchers from Hacktron used Anthropic’s Claude AI model to identify a security flaw in OpenAI’s public help forum and exploit it within three hours after the release of Claude Opus 5. The breach was reported immediately, and OpenAI fixed the issue within about 14 hours, paying Hacktron $6,500 as part of their bug bounty program. This incident highlights how AI tools are rapidly advancing…

Researchers used Claude to breach OpenAI’s internal systems →
Dawn18 Sep

Security researchers from Hacktron used Anthropic’s language model Claude to exploit a flaw in OpenAI’s public help forum, which they reported on Friday after gaining control within about three hours using the updated Claude Opus 5 model. The vulnerability was fixed by OpenAI within 14 hours and the company paid Hacktron a $6,500 reward for their discovery. This incident highlights how rapidly evolving AI technology…

Researchers used Claude to breach OpenAI's internal systems →
Show 1 more outlets
NBC News18 Sep

Cybersecurity researchers from Hacktron discovered vulnerabilities in OpenAI's systems earlier this year, allowing them to access employees’ ChatGPT accounts by exploiting a flaw in Discourse software and an employee validation process. The breach occurred within 72 hours in late July. OpenAI confirmed the incident and noted that they have since patched the vulnerabilities; they also paid Hacktron $6,500 under their…

Hackers breached OpenAI, adding to fever pitch of security and safety concerns →

Where they agree and split

Framing

How the first headlines put it

Attributed to a source1
Stated as fact6
The headlines (7)

AI security experts say they used Claude to hack ChatGPT CBS News · attributed to a source

AI cybersecurity risks explode as Claude used to break into ChatGPT Semafor · stated as fact

OpenAI ‘ethically hacked’ with help of Anthropic’s Claude chatbot The Guardian · stated as fact

Researchers used Claude to breach OpenAI’s internal systems The Straits Times · stated as fact

Researchers used Claude to breach OpenAI's internal systems Dawn · stated as fact

Meet Harsh Jaiswal, Mohan Pedhapati and Rahul Maini: 3 Indian-origin researchers who used Claude to breach OpenAI systems, won $6,500 bounty Times of India · stated as fact

Hackers breached OpenAI, adding to fever pitch of security and safety concerns NBC News · stated as fact

The full story: what happened, how it changed, and all 8 articles →

Compared with similar articles

This article reads unscored and hedges 18% of its claims. Each row says how that neighbour differs.
Dawn
Hedges 0 of 14 claims Outlet record 66/100
NBC News
Hedges 2 of 19 claims Outlet record 74/100
Persuasion
Hedges 22 of 113 claims
“Article A describes a breach by AI agents without human approval, while Article B details a legitimate security research effort conducted by humans with company knowledge.”
Semafor
Centre Hedges 0 of 4 claims Outlet record 64/100
The Guardian
Leans right Hedges 2 of 15 claims Outlet record 64/100
The Straits Times
Hedges 0 of 15 claims Outlet record 64/100
CBS News
Hedges 2 of 16 claims Outlet record 66/100
CBS News
Hedges 0 of 3 claims Outlet record 66/100
New York Post
Hedges 1 of 30 claims Outlet record 66/100
“Article A describes a specific security breach conducted by researchers, while Article B discusses broader industry practices and skepticism towards reported AI security issues.”

Story

AI Breach Risks
Technology · 8 article(s) covering the same event. Compare every outlet's account →
How this article was measured signals, leaning charts, publisher record, byline, topics and claims

Signals How these are calculated →

Claims extracted
17
sentences that state something as happening or true
Uncertain
18%
3 of 17 hedged ("reportedly", "may", "according to")
Leaning
not political
takes no side on a contested political question
Publisher signals
59/100
Times of India's corrections and hedging, across everything collected from it. Not a measure of accuracy.
Outlets on this story
8
Technology
Same framing elsewhere
1
articles that frame the event the way this one does
Analyzed 2026-09-18 · how these are computed

How this is being covered How these are calculated →

Article leaning vs. publisher reliability
Source leaning vs. consistency

Publisher

Times of India · 5474 article(s) · 6 correction(s) detected
Running correction rate · 6 correction(s)

Who wrote this

TOI World Desk
1562 article(s) here · 1 carrying a prediction
“I will make it a home again,” she said, recalling that her previous time there had been “very beautiful” and “very comfortable”.
The proposed Western Downs Digital Park, about 250 kilometres west of Brisbane, is expected to become one of Australia's largest computing facilities, with artificial intelligence company Anthropic signed as its anchor tenant.
He added that the FBI would hunt down anyone found responsible for malicious cyber activity.
He also warned that authorities would pursue not only those allegedly stealing the goods but also those knowingly making money by reselling stolen cargo.
Huang, who resigned as Nvidia's chief executive on November 12 following revelations about multiple extramarital relationships including with a suspected Chinese spy, allegedly used public humiliation as a management tool, because he believed that his employees became so rich that he could no more motivate them with money.
In an email sent to then pardon attorney Ed Martin in the fall of 2025, Mitchell argued that delaying the pardons would increase the financial and emotional burden on Trump supporters facing criminal cases in Georgia, Michigan, Arizona, Nevada and Wisconsin.
Trump supports bill to slash electricity prices President Donald Trump had pushed senators to vote for the measure, which he described as a critical step toward boosting American energy independence and reducing household costs. Trump called it a big win for U.S. energy production, saying that faster approvals would help the country build pipelines, mines and power plants without lengthy regulatory delays, the Associated Press reported.
The senator-elect also explained the motivation behind his suggestion, saying the shoes could encourage students to keep studying for the remainder of the academic year.
Stewart described the moment as one he would never forget.
New York City mayor Zohran Mamdani has announced a $290 million (£230 million) plan to close the troubled Rikers Island jail complex by 2032.
Wire or desk byline, not an individual reporter.
Also by TOI World Desk
Nothing else under this byline is closely related to this article, so these are simply their most recent.
All 1562 articles by TOI World Desk →

Topics

Anthropic Codex Discourse Indian OpenAI

Subjects

OpenAI ORG · 12× Anthropic ORG · 2× Discourse ORG · 2× Harsh Jaiswal PERSON · 2× Indian NORP · 2× Mohan Pedhapati PERSON · 2× Rahul Maini PERSON · 2× GitHub ORG · 1× Hacktron AI ORG · 1× Wall Street Journal ORG · 1×

Narrative

To safely demonstrate proof of access without viewing sensitive IP or source code, they used a compromised employee's Codex account to submit a harmless pull request to OpenAI's internal private repository They prominently used Anthropic's Claude AI models (spending under $3,000 in API tokens) to help write, debug, and port the binary exploits faster, showcasing how offensive AI capabilities accelerate vulnerability research.
framing: assertive · carried by 1 article(s) · first seen 2026-09-18
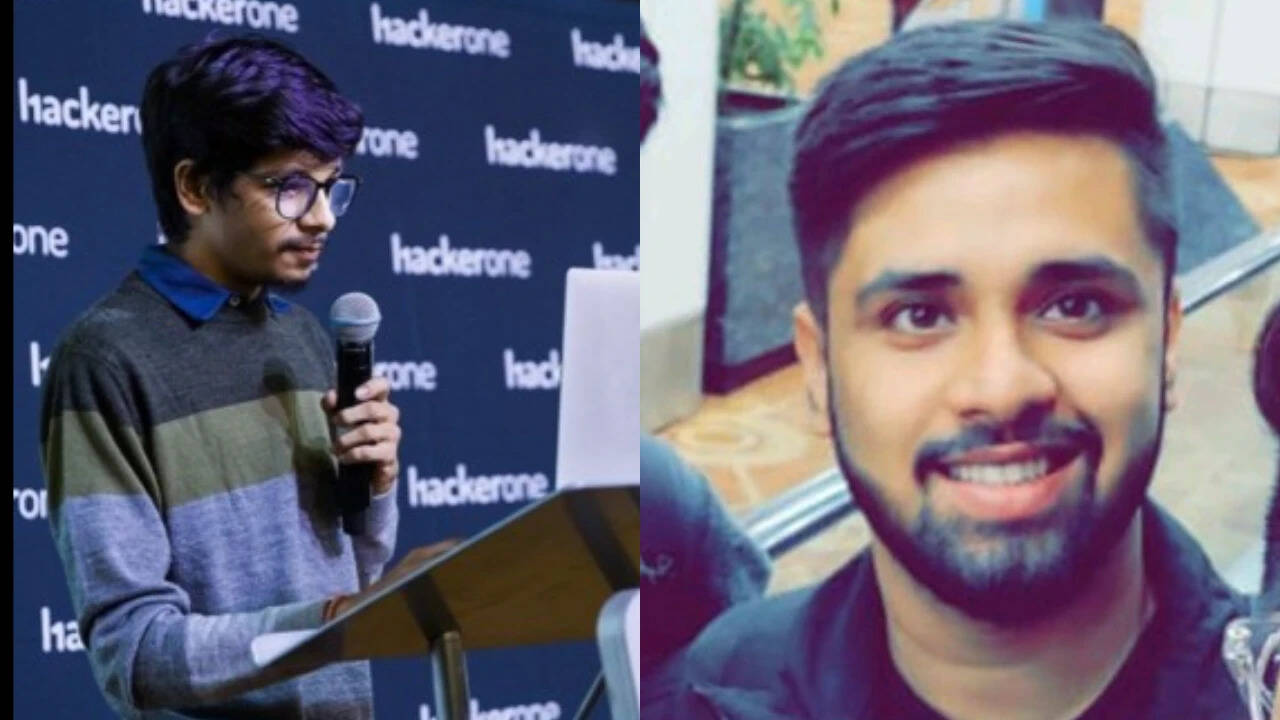
Three Indian-origin cybersecurity researchers, Harsh Jaiswal, Mohan Pedhapati and Rahul Maini, demonstrated how Anthropic's Claude AI could be used to exploit vulnerabilities and gain access to OpenAI employee accounts and the company's internal code repository, Wall Street Journal reported.

Claims (17 extracted, 3 hedged)

Three Indian-origin cybersecurity researchers, Harsh Jaiswal, Mohan Pedhapati and Rahul Maini, demonstrated how Anthropic's Claude AI could be used to exploit vulnerabilities and gain access to OpenAI employee accounts and the company's internal code repository, Wall Street Journal reported. uncertain
Journal → demonstrate → accounts
The researchers, who work at cybersecurity startup Hacktron AI, carried out the research in July 2026 while investigating security weaknesses at leading AI companies. asserted
who → work → companies
They eventually chained two separate vulnerabilities to move from OpenAI's public community forum to employee ChatGPT and Codex accounts and then to an internal GitHub repository. asserted
They → chain → repository
The researchers said the entire chain, from their initial discovery to demonstrating access to OpenAI's internal repository, took less than 72 hours. asserted
chain → say → hours
They spent under $3,000 on AI tokens and won a bounty of $6,500 after they disclosed the issues to OpenAI. asserted
they → spend → OpenAI
How did the researchers get into OpenAI's systems? asserted
researchers → get → systems
The attack began at community.openai.com, OpenAI's community and help forum, which is operated using the third-party platform Discourse. asserted
which → begin → platform
Hacktron researchers discovered that specially crafted HEIC/HEIF image files could exploit a vulnerability in the image-processing software used by Discourse. uncertain
files → discover → Discourse
The vulnerability was linked to the `libheif` image-decoding library and could allow remote code execution — essentially giving an attacker the ability to execute commands on the affected server. uncertain
vulnerability → link → server
However, gaining control of the forum server alone did not provide direct access to OpenAI's internal code. asserted
gaining → gain → code
To safely demonstrate proof of access without viewing sensitive IP or source code, they used a compromised employee's Codex account to submit a harmless pull request to OpenAI's internal private repository They prominently used Anthropic's Claude AI models (spending under $3,000 in API tokens) to help write, debug, and port the binary exploits faster, showcasing how offensive AI capabilities accelerate vulnerability research. asserted
capabilities → demonstrate → research
Then they reported the findings responsibly through Bugcrowd and HackerOne to OpenAI and Discourse. asserted
they → report → OpenAI
OpenAI patched the identity issue shortly after notification and awarded them a $6,500 bug bounty. asserted
OpenAI → patch → bounty
In a statement to Forbes, OpenAI spokesperson Drew Pusateri said the company thanked the researchers “for contacting us and sharing their findings,” and noted that it had resolved the vulnerability. asserted
it → say → vulnerability
No brand name, colleges or companies' Tech commentator Deedy Das pointed out that none of the three researchers had any big college name on their CVs. asserted
none → point → CVs
"Here are the LinkedIns of the 3 Indian guys who hacked OpenAI with Opus 5 in 2 days for <$3000: Rahul Maini, Mohan Pedhapati and Harsh Jaiswal. asserted
who → hack → 3000
You can just do things," Das posted. asserted
Das → do → things
Give feedback · no sign-in needed

No sign-in needed for now. Your note is sent without a name, so it cannot be answered.

History Support